Penetration testing for stronger cybersecurity
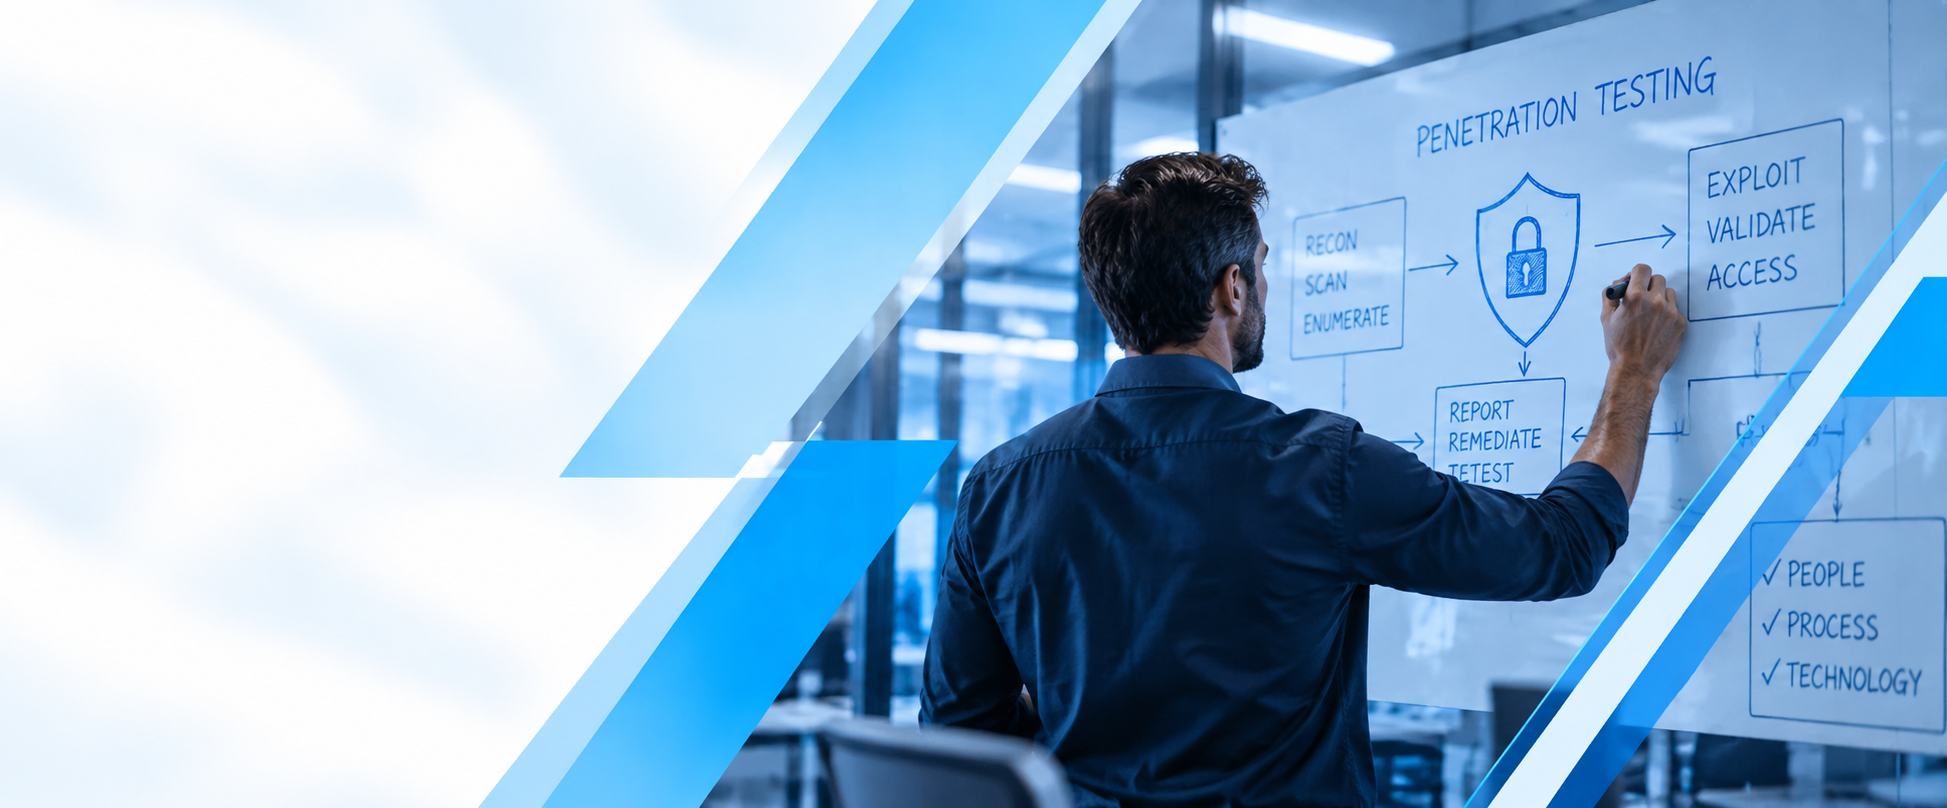
Cyber threats continue to evolve, and security controls alone cannot guarantee protection. Penetration testing helps organizations identify exploitable weaknesses, validate their defenses and make informed decisions about reducing cybersecurity risk.
Penetration testing that identifies risks before attackers do
Organizations invest heavily in cybersecurity, but understanding whether those defenses can withstand a real-world attack requires more than routine monitoring or automated vulnerability scans. Penetration testing evaluates potential attack paths, identifies weaknesses that could be exploited and provides actionable intelligence to help security teams prioritize remediation and strengthen their overall security posture.
Network penetration testing
Evaluate internal and external network environments to identify exploitable weaknesses, insecure configurations and potential paths to critical systems.
Application security testing
Assess web applications and connected systems for security vulnerabilities that could expose sensitive information or enable unauthorized access.
Cloud security testing
Examine cloud environments, access controls and configurations to identify weaknesses that could compromise business applications or information.
Microsoft 365 security testing
Evaluate identity configurations, access permissions and Microsoft 365 security controls to identify potential exposure within your productivity environment.
Penetration testing that strengthens your cybersecurity posture
Understanding your vulnerabilities before attackers exploit them is essential to protecting your organization. Penetration testing provides a structured evaluation of potential security weaknesses, helping technology leaders prioritize remediation, validate existing controls and make informed decisions about cybersecurity investments.
-
Identify exploitable vulnerabilities
Discover weaknesses across networks, applications and infrastructure that could expose critical systems or sensitive business information.
-
Validate security investments
Evaluate the effectiveness of existing security controls and identify where additional protection or remediation may be required.
-
Prioritize security remediation
Focus technical resources on the vulnerabilities presenting the greatest potential risk to business operations and information assets.
-
Support compliance requirements
Generate documented security findings that can support audit preparation, regulatory obligations and customer security assessments.
-
Reduce business disruption
Identify potential attack paths before they contribute to operational interruptions, data exposure or costly security incidents.
-
Strengthen cyber resilience
Use actionable findings to improve security controls, guide future investments and strengthen your organization’s overall readiness.
Understand your security exposure
Start with a complimentary IT and security assessment from Unimatrix. Our team reviews your existing infrastructure, security configurations, software investments and potential risks, then provides a written report with prioritized recommendations and a 45-minute walkthrough. Understand where your organization may be exposed and what deserves attention before investing in further security testing or remediation. The report is yours to keep, with no obligation to proceed.
FAQs
Penetration testing can support cybersecurity compliance and assurance activities by providing documented evidence that an organization has evaluated selected systems for exploitable security weaknesses.
However, penetration testing does not automatically establish compliance with a law, regulation, contractual requirement or security standard.
Compliance involves multiple elements, including organizational policies, employee practices, access controls, technical safeguards, documentation, monitoring and incident response procedures.
The role of penetration testing is to evaluate whether selected technical controls and configurations can withstand defined attack scenarios.
For organizations subject to customer security questionnaires, penetration testing may help answer questions about security validation, vulnerability management and independent assessment activities.
Enterprise customers may request recent testing reports or summaries before approving a supplier that handles sensitive information or connects to important systems.
Similarly, cyber insurers may ask about vulnerability assessments, security testing and the remediation of identified weaknesses.
For healthcare organizations in Ontario, security testing may contribute to the technical safeguards used to protect sensitive information. However, obligations under PHIPA extend beyond testing and require broader privacy and security practices.
Professional services firms may face contractual security requirements from clients, while manufacturers and distributors may be required to demonstrate cybersecurity practices as part of supplier qualification.
A useful penetration testing report should document the testing scope, findings, severity, potential business impact and recommended remediation activities.
Organizations should also maintain records showing how significant findings were addressed.
Unimatrix's Citadel Security platform complements testing through monitoring, incident response planning and documented security practices. Its managed cybersecurity services can support the ongoing security activities that exist beyond a single assessment.
Organizations should confirm their specific compliance obligations with qualified legal, regulatory or assurance professionals before determining the appropriate testing program.
Penetration testing can help organizations identify weaknesses that attackers might exploit to gain access to systems, expand their privileges or move through a network.
These activities are relevant to ransomware attacks, which frequently involve compromised accounts, exposed services, unpatched vulnerabilities or weaknesses in network security.
However, penetration testing does not guarantee that ransomware or other cybersecurity incidents will be prevented.
Its value lies in helping organizations identify and address potential attack paths before they are exploited.
For example, a penetration test may identify an exposed remote access service, an account with excessive permissions or a configuration that could allow an attacker to move between systems.
These findings can be especially important for organizations whose operations depend on continuous access to technology.
Manufacturers and distributors may experience production or shipping interruptions when critical systems become unavailable. Healthcare organizations may lose access to applications supporting patient care. Professional services firms may face disruption to client work and exposure of confidential information.
The business impact of a security incident therefore extends beyond the immediate technical problem.
For CIOs and technology leaders, penetration testing can provide additional information for prioritizing remediation and evaluating security investments.
For business executives, it can help clarify which weaknesses could contribute to significant operational disruption.
A resilient cybersecurity strategy must also include capabilities that penetration testing does not provide, such as ongoing monitoring, incident response planning, tested backups and recovery procedures.
Unimatrix's managed IT services include infrastructure management, patching and backups, while managed cybersecurity services provide additional threat monitoring and incident response preparation.
Together, these activities support a broader approach to reducing cyber risk and improving business continuity.
Microsoft 365 and cloud technologies have become central to business operations, making identity management, access permissions and cloud configuration increasingly important cybersecurity considerations.
Traditional network security controls remain relevant, but many modern attacks target user identities, cloud applications and the permissions connecting different systems.
Penetration testing and authorized security assessments can help organizations identify weaknesses in these environments.
For Microsoft 365, important considerations include multifactor authentication, privileged account access, conditional access configurations, application permissions and the ways users access sensitive business information.
A compromised account may expose email, documents, collaboration environments or connected applications without requiring an attacker to breach a traditional corporate network.
Cloud environments introduce additional considerations. Misconfigured storage, excessive permissions, exposed services and insecure application connections can create opportunities for unauthorized access.
The objective of testing is to determine whether these weaknesses could create meaningful exposure within the authorized assessment scope.
Testing Microsoft and cloud environments also requires careful planning. Some techniques may be restricted by platform policies, and testing should be conducted only against systems and resources for which the organization has appropriate authorization.
For CIOs and IT directors, the findings can help prioritize identity security improvements, configuration changes and additional controls.
Cloud security testing is especially relevant as organizations introduce more connected applications and AI-enabled workflows. AI tools may interact with information already accessible through existing permissions, making identity governance and data access controls increasingly important.
Unimatrix's Elevate platform includes Microsoft 365 management and baseline security capabilities, while Citadel Security provides additional monitoring and risk-management services.
Explore Unimatrix's managed IT services and managed cybersecurity to understand how Microsoft and cloud environments fit within a broader security strategy.
The cost of penetration testing in Canada varies considerably depending on the systems being tested, the complexity of the environment, the testing methodology and the depth of assessment required.
Unlike standardized software subscriptions, penetration testing is generally scoped around a defined set of technical and business requirements.
Several factors influence pricing.
Testing scope: Assessing a small number of external systems generally requires less effort than evaluating a complex environment with multiple networks, applications and locations.
Application complexity: Web applications with authentication, sensitive information, integrations and multiple user roles may require more extensive testing.
Cloud and identity environments: Testing cloud configurations, Microsoft 365 environments and identity management systems may require specialized expertise and additional preparation to ensure testing remains within authorized boundaries.
Testing methodology: Automated scanning, manual vulnerability validation and controlled exploitation require different levels of effort. A comprehensive penetration test generally involves more investigation than an automated vulnerability assessment.
Reporting requirements: Organizations may require executive summaries, detailed technical findings, remediation recommendations, evidence for compliance reviews and subsequent retesting.
Operational considerations: Healthcare environments, manufacturing systems and business-critical applications may require additional coordination to minimize the possibility of operational disruption.
For CIOs and IT directors, penetration testing should be evaluated as a risk-management investment rather than simply a technical expense. The lowest-cost assessment may not provide sufficient depth to evaluate the organization's most important security concerns.
A useful proposal should clearly identify what will be tested, which methods are permitted, the expected deliverables, any exclusions and whether remediation validation is included.
Organizations should also distinguish the cost of identifying vulnerabilities from the cost of correcting them. Remediation may require configuration changes, software updates, infrastructure improvements or additional security controls.
Unimatrix offers a complimentary IT and security assessment that can help organizations understand their existing technology environment and identify areas requiring further investigation. Specialized penetration testing requirements can then be discussed and scoped separately.
Learn more about Unimatrix's managed cybersecurity services and how ongoing security management complements targeted penetration testing.
The appropriate frequency of penetration testing depends on an organization's technology environment, business risk, regulatory obligations and rate of technological change.
For many organizations, annual penetration testing is a useful planning baseline. However, this should not be interpreted as a universal requirement or a guarantee that annual testing is sufficient.
Businesses operating critical systems, processing sensitive information or maintaining complex cloud and application environments may require more frequent testing.
Significant technology changes can also create reasons to conduct additional penetration testing outside a regular schedule.
Examples include deploying a new customer-facing application, migrating infrastructure to the cloud, implementing major network changes, acquiring another organization or introducing new remote access capabilities.
For CIOs and IT directors, the decision should be based on risk rather than an arbitrary calendar interval.
An organization that changes its technology environment frequently may accumulate new security exposure faster than one operating a relatively stable infrastructure.
External obligations may also influence testing frequency. Enterprise customers sometimes require suppliers to provide evidence of recent penetration testing. Certain security standards, contracts and regulatory frameworks may specify testing expectations.
It is important to distinguish these requirements from general recommendations. The exact testing frequency and scope should be determined by the organization's applicable obligations and risk profile.
Penetration testing should also be coordinated with remediation activities. If a previous assessment identified significant weaknesses, targeted retesting may be appropriate after corrective work has been completed.
A broader cybersecurity program should combine periodic testing with ongoing monitoring, patch management, identity security and incident readiness.
Unimatrix's managed IT services support the operational management of infrastructure and technology environments, while managed cybersecurity adds monitoring and risk-management capabilities that complement periodic security testing.
Selecting a penetration testing provider in Toronto requires evaluating technical expertise, testing methodology, industry experience and the provider's ability to translate security findings into meaningful business recommendations.
For CIOs and IT directors, the primary concern is whether the assessment will accurately evaluate the organization's security exposure. For CEOs, CFOs and other business leaders, the objective is to understand how potential vulnerabilities could affect operations, financial performance, customer relationships and business continuity.
A qualified penetration testing provider should begin by understanding the organization's environment and establishing a clearly defined scope.
Technical expertise is an important consideration. Organizations should evaluate the testing team's experience with the technologies being assessed, including networks, web applications, cloud infrastructure, identity systems and Microsoft environments where applicable.
Testing methodology should also be examined. Ask whether the engagement includes manual testing, how potential vulnerabilities are validated and which recognized testing methodologies or frameworks inform the assessment.
Professional qualifications can provide additional assurance. Relevant certifications, demonstrable technical experience and appropriate professional liability coverage may help organizations evaluate potential providers.
Operational safeguards are particularly important when testing business-critical systems. The provider should establish written authorization, testing boundaries, communication procedures and escalation protocols before work begins.
Reporting quality is another major consideration. A penetration testing report should provide clear technical findings, explain potential business impact and identify practical remediation priorities. Executive stakeholders should be able to understand the significance of the results without needing to interpret complex technical evidence.
Finally, consider what happens after testing. Identifying vulnerabilities is only the first step. Organizations need a process for assigning remediation responsibilities, implementing corrective actions and validating that significant weaknesses have been addressed.
For organizations across Toronto and the Greater Toronto Area, penetration testing should form part of a broader cybersecurity strategy that includes ongoing monitoring, infrastructure management, incident response planning and business continuity.
Unimatrix approaches cybersecurity through its Citadel Security platform, which combines vulnerability monitoring, managed detection and response, incident response planning and documented security practices.
Organizations evaluating their security posture can begin with a complimentary IT and security assessment to identify existing risks and determine which areas may warrant specialized testing.
Explore Unimatrix's managed cybersecurity services and managed IT services to understand how security testing can fit into a coordinated approach to technology risk management.
Penetration testing is a structured cybersecurity assessment in which authorized security professionals simulate potential attacks against an organization's systems, networks or applications to identify weaknesses that could be exploited by a malicious actor.
Unlike general security monitoring, penetration testing is designed to evaluate how security controls perform when challenged. It can reveal weaknesses in configurations, access permissions, authentication mechanisms, software and the connections between different systems.
For CIOs and IT directors, penetration testing provides evidence that can help validate existing security investments and identify areas requiring additional attention. For CEOs and business owners, it offers a clearer understanding of how technical weaknesses could affect operations, sensitive information, customer relationships and business continuity.
The importance of penetration testing has increased as organizations adopt cloud applications, hybrid infrastructure, remote access technologies and interconnected business systems. Each additional application or connection can introduce potential exposure that may not be obvious during routine IT management.
A penetration test may examine how an attacker could gain initial access, whether that access could be expanded and which systems or information might be affected. The findings should distinguish between theoretical weaknesses and vulnerabilities that present credible exploitation risks.
Penetration testing is also relevant to organizations facing cybersecurity requirements from enterprise customers, insurers or regulatory frameworks. While a test does not automatically establish compliance, documented findings can support security reviews and demonstrate that potential weaknesses are being evaluated.
Most importantly, penetration testing should lead to action. Identifying vulnerabilities is valuable only when organizations use the findings to prioritize remediation and strengthen security controls.
Unimatrix's managed cybersecurity services provide complementary security capabilities, including monitoring, vulnerability management and incident response planning, that can help organizations address broader security requirements.
Penetration testing and vulnerability scanning are complementary cybersecurity practices, but they answer different questions about an organization's security posture.
Vulnerability scanning uses automated tools to identify known weaknesses in systems, software, network devices and configurations. These scans may detect missing security updates, exposed services, outdated software or settings associated with known security vulnerabilities.
The primary objective is broad visibility into potential weaknesses.
Penetration testing takes a more investigative approach. Authorized security professionals examine whether identified weaknesses can be exploited and what an attacker might accomplish by combining multiple vulnerabilities or configuration problems.
For example, a vulnerability scan might identify an exposed service or an outdated software component. A penetration test may determine whether that exposure could allow unauthorized access, privilege escalation or movement into other parts of the environment.
This distinction matters because not every vulnerability presents the same level of business risk. Some findings may be difficult to exploit, while others could expose critical information or systems even if their technical severity initially appears moderate.
Penetration testing can therefore help organizations prioritize remediation based on credible attack scenarios rather than relying exclusively on automated severity scores.
However, penetration testing is not a replacement for ongoing vulnerability management. A penetration test evaluates a defined scope during a particular period. New vulnerabilities can emerge afterward as software changes, systems are added and new threats are discovered.
Organizations generally benefit from combining periodic penetration testing with continuous or scheduled security monitoring.
Unimatrix's Citadel Security platform includes quarterly external vulnerability scanning as part of its managed cybersecurity services. This provides ongoing visibility into externally exposed weaknesses and supports a broader approach to cybersecurity risk management.
A penetration testing report should provide both technical findings and sufficient business context to help an organization understand its security exposure and determine appropriate next steps.
The most useful reports do more than list vulnerabilities. They explain what was tested, what was discovered, why the findings matter and how the organization can address them.
A typical report should begin with an executive summary that describes the testing objectives, scope and most significant findings in language accessible to business and technology leadership.
This is particularly important for organizations where cybersecurity investment decisions involve CIOs, CFOs, executive teams or boards of directors.
The technical section should document the systems evaluated, the testing approach, identified vulnerabilities and the evidence supporting each finding.
Where exploitation was authorized and demonstrated, the report should distinguish verified results from potential or theoretical weaknesses.
Findings should also include severity assessments and remediation recommendations.
However, technical severity alone may not determine business priority. A vulnerability affecting a critical production system may require different treatment from a similar weakness in a low-impact environment.
A strong report should therefore help organizations consider operational importance, potential exposure and remediation complexity.
For IT and security teams, clear technical guidance supports corrective action. For executives, an understandable summary supports investment decisions and oversight.
Testing reports should also document limitations, exclusions and any systems that were outside the authorized scope.
After remediation, organizations may choose to conduct targeted retesting to verify that significant weaknesses have been addressed.
Unimatrix's managed IT services and managed cybersecurity services provide complementary operational and security capabilities that can support the broader remediation and risk-management process.
The scope of a penetration test should reflect the systems, applications and information that are most important to the organization's operations and security objectives.
There is no single testing scope that is appropriate for every business.
For some organizations, externally accessible infrastructure represents the highest priority. This may include firewalls, remote access systems, internet-facing servers and other services accessible from outside the corporate network.
Other organizations may need to prioritize web applications, cloud environments, identity systems or internal networks.
A comprehensive scoping discussion should consider several areas.
External infrastructure: Systems and services accessible from the internet, including remote access technologies and network security devices.
Internal networks: Infrastructure and systems that could be exposed if an attacker gained access through a compromised employee account or device.
Web applications: Customer portals, business applications and websites that process information or provide access to sensitive functionality.
Cloud environments: Cloud-hosted applications, infrastructure configurations, permissions and connected services.
Identity and access systems: Authentication mechanisms, privileged accounts and access controls that determine what users can reach.
Microsoft environments: Microsoft 365 and related identity configurations where inappropriate permissions or insecure settings could expose business information.
The testing scope should also account for operational sensitivity. Healthcare systems, manufacturing environments and critical business applications may require special precautions to avoid unnecessary disruption.
Before testing begins, the organization and testing provider should agree on authorized targets, permitted techniques, timing, exclusions and reporting expectations.
A narrowly scoped penetration test can provide valuable information, but it should not be represented as an assessment of systems that were not included.
Unimatrix's managed IT services and managed cybersecurity services address the underlying infrastructure and security management functions that support an organization's broader testing and remediation strategy.